NIS2 changes cybersecurity from an IT concern into a business-management responsibility.
It affects how companies manage risk, suppliers, access rights, incidents, continuity, and proof of control.
For many organisations, the first question is: “Does NIS2 apply to us?” The more useful question is: “Could a cyber incident stop us from delivering products, paying suppliers, serving customers, or meeting legal obligations?” If the answer is yes, NIS2 should influence how the company operates—even if it is not directly regulated today.
NIS2 is the EU’s updated cybersecurity directive. Formally called Directive (EU) 2022/2555, it replaced the original NIS Directive and created a common cybersecurity framework across the EU. It covers 18 critical sectors, expands the number of organisations in scope, and introduces stronger supervision, incident-reporting duties, and management accountability. Read the official Directive and the European Commission’s NIS2 overview.
“Cybersecurity is no longer only about protecting systems. It is about protecting the company’s ability to operate.”
NIS2 at a glance
| Topic | What NIS2 requires in practice |
|---|---|
| Scope | Medium and large entities in designated critical sectors, plus certain smaller organisations with a high societal or economic impact |
| Leadership | Management must approve cybersecurity measures, oversee implementation, and receive appropriate training |
| Risk management | Companies must use proportionate technical, operational, and organisational security measures |
| Incidents | Significant cyber incidents must be reported quickly through national channels |
| Supply chain | Vendors, service providers, software, and managed IT partners become part of the cybersecurity risk picture |
| Enforcement | National authorities can inspect, audit, request evidence, issue binding instructions, and impose fines |
| Business impact | Cybersecurity becomes connected to procurement, continuity planning, finance, operations, HR, manufacturing, and customer service |
The Directive entered into force in January 2023. EU Member States were required to transpose it into national law by 17 October 2024, and NIS1 was repealed from 18 October 2024. European Commission.
NIS2 in Bulgaria: the current position
Bulgaria adopted amendments to its Cybersecurity Act to implement NIS2. The law was adopted by the National Assembly on 5 February 2026 and published in the State Gazette on 13 February 2026. It establishes the Bulgarian scope, differentiates between essential and important entities, and sets national reporting duties and transition steps. Official State Gazette text.
The Bulgarian law covers public authorities and private or public entities in the sectors listed in its annexes when they meet the size criteria for medium-sized enterprises or larger. It can also apply regardless of company size where a business is the sole provider of an essential service, its disruption could materially affect public safety or health, or it is critical at national or regional level. Bulgarian Cybersecurity Act amendment.
This matters because the answer is not simply “we have fewer than 250 employees, so NIS2 does not apply.” Size is important, but it is not the only test. Sector, service criticality, dependencies, and national designation also matter.
The Bulgarian transition timetable includes the designation of competent authorities, implementation rules, and identification of essential and important entities. Companies should therefore monitor notices from the relevant authority and seek legal advice for a formal scope determination.
Does NIS2 apply to every company?
No—not every company is directly regulated by NIS2. However, nearly every company will feel its effect through customers, suppliers, insurers, banks, tenders, and contractual security questionnaires.
A small furniture manufacturer may not fall directly within the Directive. But if it supplies a regulated manufacturer, public body, utility, hospital, or digital-service provider, it may be asked to demonstrate:
- who can access its systems and ERP data;
- whether backups are tested;
- how it handles a ransomware incident;
- what happens if a supplier, cloud provider, or warehouse system fails;
- how it reviews third-party software and IT partners;
- whether its management has approved cybersecurity policies.
That is why NIS2 is best understood as a market-wide resilience standard, not just a legal issue for a narrow group of companies.
| Company profile | Likely NIS2 position | What to do now |
|---|---|---|
| Large energy, transport, healthcare, water, digital infrastructure, telecom, or managed IT provider | Often directly in scope; may be an essential entity | Complete formal legal scope assessment and build an evidence-based compliance program |
| Medium or large manufacturer in covered categories, food producer, waste-management business, postal/courier provider, online marketplace, research organization | May be directly in scope as an important entity | Review sector classification, company size, national designation, and reporting obligations |
| Small supplier to a regulated company | Often indirectly affected through contracts and supply-chain requirements | Establish a security baseline and prepare evidence for customer due diligence |
| General SME outside listed sectors | Usually not directly in scope, unless specifically designated | Use NIS2 as a practical resilience framework rather than waiting for a customer incident |
Which sectors are in scope?
NIS2 distinguishes between sectors of high criticality and other critical sectors. The exact legal classification should always be reviewed against the Directive and the relevant national law.
| High-criticality sectors | Other critical sectors |
|---|---|
| Energy | Postal and courier services |
| Transport | Waste management |
| Banking | Chemicals |
| Financial market infrastructure | Food production, processing, and distribution |
| Health | Manufacturing of certain critical products |
| Drinking water and wastewater | Digital providers such as online marketplaces, search engines, and social platforms |
| Digital infrastructure | Research organizations |
| ICT service management, including managed service and managed security service providers | |
| Public administration | |
| Space |
For manufacturing, the scope is particularly relevant for businesses involved in areas such as medical devices, electronics, electrical equipment, machinery, motor vehicles, and other transport equipment. European Commission sector overview.
Essential versus important entities
NIS2 separates regulated organizations into two groups. Both must manage cybersecurity risk and report significant incidents. The main difference is how supervision is carried out and how strict the enforcement approach may be.
| Category | Typical profile | Supervision approach |
|---|---|---|
| Essential entity | Larger entities in high-criticality sectors, certain digital infrastructure providers, public bodies, or specifically designated critical organizations | More proactive supervision, including regular and targeted audits |
| Important entity | Other covered medium and large entities, including many businesses in Annex II sectors | Usually supervised after evidence of non-compliance or an incident, though national authorities retain strong powers |
This distinction should not create false comfort. An “important” entity still needs a serious cybersecurity program. Its systems may be inspected, evidence can be requested, and failure to meet duties can trigger sanctions.
The European Commission explains that authorities may carry out audits, on-site and off-site checks, request documents and evidence, and issue binding instructions. NIS2 FAQ.
The core idea: risk management, not a checkbox exercise
NIS2 does not tell every company to buy one named product or use one exact technology. Instead, it requires appropriate and proportionate cybersecurity risk-management measures.
That wording is important. A small supplier and a national energy operator do not face the same risks. But both must understand their important systems, likely threats, critical suppliers, recovery needs, and decision-making responsibilities.
Article 21 of NIS2 sets out the core areas companies need to address.
| NIS2 risk area | The practical business question |
|---|---|
| Risk analysis and security policies | Do we know our key systems, risks, owners, and security rules? |
| Incident handling | Who detects, contains, investigates, communicates, and documents an incident? |
| Business continuity | Can we continue operating if systems are unavailable? Are backups, recovery, and crisis procedures tested? |
| Supply-chain security | Do we assess the security of software providers, hosting partners, IT service companies, and critical vendors? |
| Secure development and vulnerability management | Are systems patched, configured securely, and reviewed for weaknesses? |
| Security effectiveness | Do we test whether controls actually work—not merely whether policies exist? |
| Cyber hygiene and training | Do employees know how to identify phishing, protect credentials, and report suspicious activity? |
| Cryptography and encryption | Is sensitive information protected appropriately in storage and transit? |
| Access control and asset management | Does each user have only the access they need? Do we know what systems, devices, and data we own? |
| Multi-factor authentication and secure communications | Are high-risk accounts and remote access protected by stronger authentication? |
The strongest NIS2 program are not built around a policy folder. They are built around operational proof.
A policy saying “we back up our systems” is weak if no one can show when restoration was last tested. A supplier policy is weak if critical IT providers have never been assessed. An access-control rule is weak if former employees still have active accounts.
The board and management are accountable
One of NIS2’s biggest changes is that it brings cybersecurity firmly into the boardroom.
Management bodies must approve cybersecurity risk-management measures, oversee their implementation, and can be held accountable for failures to comply. The Directive also requires management members to undertake training so they can identify risks and understand cybersecurity practices. European Commission NIS2 overview.
This does not mean every CEO must become a security engineer. It means leadership must be able to ask—and receive clear answers to—the right questions:
- What would stop production, deliveries, invoicing, payroll, or customer support?
- Which systems are business-critical?
- Which suppliers have privileged access to our data or infrastructure?
- When were backups and disaster recovery last tested?
- How quickly can we recognize and report a significant incident?
- Who has the authority to stop a process, isolate systems, or communicate with customers?
- What evidence could we show an auditor tomorrow?
| Management responsibility | Good evidence |
|---|---|
| Approve risk-management approach | Signed policy, board minutes, clear ownership |
| Monitor cyber risk | Regular dashboard with key risks, incidents, vulnerabilities, backup tests, and supplier status |
| Fund critical remediation | Budget decisions linked to documented risks |
| Ensure training | Training records for management and relevant employees |
| Review business continuity | Tested recovery plans, lessons learned, updated procedures |
| Oversee suppliers | Security requirements, contracts, reviews, and escalation paths |
Incident reporting: the clock starts early
NIS2 introduces strict reporting expectations for significant incidents. Under the Bulgarian law, essential and important entities report to CERT Bulgaria (СЕРИКС) through a staged process. Official Bulgarian requirements.
| Time from becoming aware of a significant incident | Expected action |
|---|---|
| Within 24 hours | Submit an early warning. State, where relevant, whether the incident may involve unlawful or malicious activity and whether it could have cross-border effects. |
| Within 72 hours | Submit an incident notification with an initial assessment of severity, impact, and available technical details. |
| When requested | Provide progress or intermediate reports. |
| Within one month | Provide a final report describing the incident, likely cause, impact, mitigation actions, and any cross-border effects. If unresolved, provide an interim report and submit the final report within one month of resolution. |
ENISA likewise describes the 24-hour early-warning and 72-hour incident-notification stages as central NIS2 reporting duties. ENISA incident-reporting overview.
This is why incident response cannot begin when a lawyer or executive is finally available. A company must know in advance what counts as a significant incident, who makes the initial classification, and how evidence will be collected.
A realistic ransomware scenario
Imagine a manufacturer discovers at 08:00 on Monday that users cannot access the ERP, warehouse terminals, or production planning system.
The first priority is not writing a report. It is to protect people, contain the incident, preserve evidence, and keep critical operations moving safely. But the reporting clock has already started.
| Period | Operational response |
|---|---|
| 0–4 hours | Isolate affected systems, activate the incident team, preserve logs, identify affected services, and assess whether operations can continue manually |
| 4–24 hours | Determine whether the incident is significant, prepare the early warning, inform essential internal stakeholders, and begin customer/supplier impact assessment |
| 24–72 hours | Deepen technical investigation, confirm business impact, identify likely attack path, report initial severity and mitigation measures |
| Days 4–30 | Recover systems, validate data, document decisions, improve controls, complete the final report |
A reporting deadline is not a recovery plan. The company needs both.
Penalties: serious enough to change behavior
NIS2 requires Member States to provide for meaningful administrative fines. At EU level, the Directive sets minimum maximum fine levels:
| Entity type | Minimum maximum administrative fine required by NIS2 |
|---|---|
| Essential entity | At least €10 million or 2% of total worldwide annual turnover, whichever is higher |
| Important entity | At least €7 million or 1.4% of total worldwide annual turnover, whichever is higher |
National laws determine the detailed enforcement rules and actual application. Authorities must consider the circumstances of each case, including severity, duration, damage, and whether the infringement was intentional or negligent. European Commission FAQ.
The more immediate business risk is often not the fine. It is the operational cost of an attack: halted production, unavailable warehouse processes, missed deliveries, recovery work, reputational damage, lost data, delayed invoices, and difficult customer conversations.
NIS2, GDPR, DORA, and the Cyber Resilience Act: do not mix them up
Companies often hear several EU digital laws at once. They overlap, but they do not mean the same thing.
| Framework | Main focus | Typical question it answers |
|---|---|---|
| NIS2 | Cybersecurity resilience of critical and important entities | Can this organization prevent, manage, recover from, and report cyber incidents? |
| GDPR | Protection of personal data | Are we processing personal data lawfully and protecting it appropriately? |
| DORA | Digital operational resilience in financial services | Can financial entities withstand ICT disruption and manage ICT third-party risk? |
| Cyber Resilience Act | Cybersecurity requirements for products with digital elements | Is this connected product or software secure throughout its lifecycle? |
| ISO 27001 | Voluntary information-security management standard | Do we have a structured, auditable information-security management system? |
A company can comply with GDPR and still fail NIS2. For example, it may handle personal data correctly but have weak recovery planning, poor supplier oversight, or unmanaged operational systems.
Likewise, ISO 27001 certification can provide a strong foundation, but it does not automatically prove NIS2 compliance. NIS2 requires sector-specific, legal, operational, and reporting readiness.
Why ERP is central to NIS2 readiness
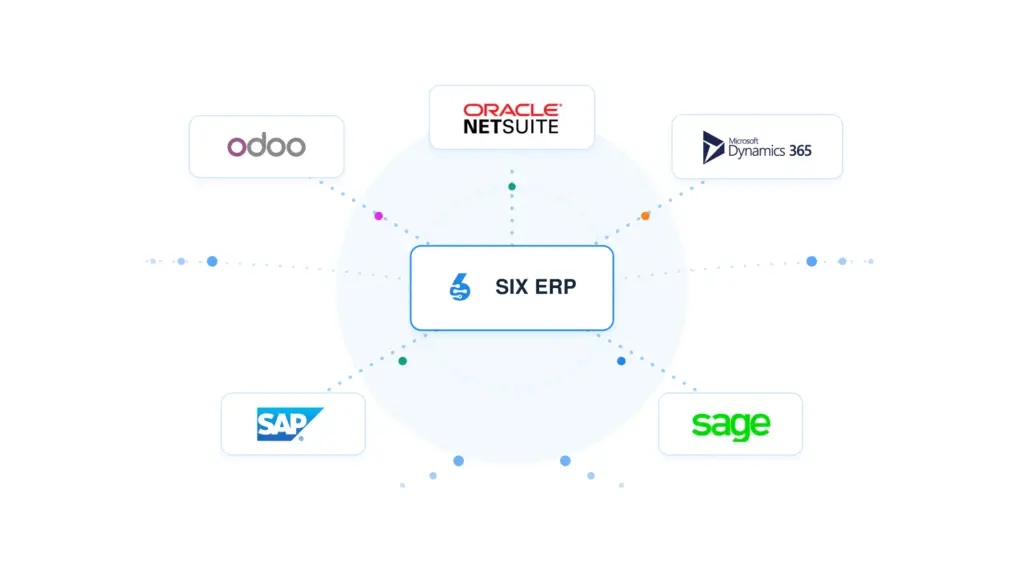
ERP is often the operational heart of the business. It holds or connects customer records, suppliers, purchasing, inventory, production planning, finance, invoices, warehouse movements, quality data, service operations, and employee workflows.
If ERP access is lost, incorrect, manipulated, or unavailable, the company may not be able to answer basic questions:
- What stock do we have?
- Which purchase orders are open?
- Which deliveries are due today?
- Which production orders can still run?
- Which suppliers must be contacted?
- Which customer commitments are at risk?
- Which invoices, payments, or payroll activities are affected?
- What changed before the incident?
This is why NIS2 is not only a firewall, endpoint-security, or IT-infrastructure topic. It is also a process-control and business-continuity topic.
How SIX ERP can support NIS2-related controls
SIX ERP cannot make a company “NIS2 compliant” on its own. NIS2 requires broader controls across people, devices, networks, cloud services, suppliers, policies, training, and incident response.
However, an integrated ERP can be an important part of the evidence and control environment.
| NIS2 need | How SIX ERP can support the process |
|---|---|
| Controlled access | Role-based access and clear user permissions help reduce unnecessary access to commercial and operational data |
| Accountability | Audit trails and change history can support investigation of who changed key records, approvals, or transactions |
| Asset and process visibility | Centralized information across purchasing, inventory, manufacturing, finance, CRM, and warehousing reduces dependence on disconnected spreadsheets |
| Supplier risk management | Supplier records, purchasing history, contracts, approvals, and performance data can support structured vendor oversight |
| Business continuity | Clear operational data and process documentation make it easier to identify critical workflows and plan manual or recovery procedures |
| Incident investigation | Central records can help identify affected orders, customers, inventory movements, invoices, or production plans |
| Segregation of duties | Approval workflows and role separation can reduce the risk of unauthorized purchasing, payment, or master-data changes |
| Evidence for audits | Reporting and structured data help the company demonstrate processes, controls, ownership, and historical activity |
The real value is not simply storing information in one place. It is being able to understand the operational impact of a disruption quickly.
For example, if a cyber incident affects warehouse operations, management should be able to identify priority customer orders, stock availability, delayed deliveries, alternative fulfilment options, and affected suppliers. With disconnected systems, that work becomes slower exactly when the business can least afford delay.
A practical NIS2 readiness roadmap
The goal is not to create a giant cybersecurity project that never finishes. Start with the operational risks that could materially affect your company.
First 30 days: establish ownership and scope
Appoint an executive owner and form a small cross-functional group covering management, IT, finance, operations, HR, procurement, and legal/compliance. Determine whether the organization is directly in scope and document the reasoning.
At the same time, identify the systems that matter most: ERP, email, identity systems, finance, warehouse tools, production systems, cloud storage, backups, remote access, and critical supplier portals.
If you cannot map your critical systems and dependencies, you cannot manage their risk.
Days 31–60: assess risk and close obvious gaps
Review access rights, former-user accounts, backup coverage, patching, endpoint protection, remote access, supplier contracts, incident contacts, and recovery procedures.
This is also the time to identify “single points of failure.” Perhaps only one person understands a critical ERP integration. Perhaps the warehouse relies on one internet line, or invoices arrive in a shared mailbox with no ownership. These are operational risks, not just technical risks.
Days 61–90: test the plan
Run a short tabletop exercise. Do not make it theoretical.
Ask: “It is Monday morning. ERP and email are unavailable after a suspected ransomware attack. What do we do in the first hour? Who decides? How do we take orders? How do we communicate with customers? What needs to be reported?”
Then test whether backups can actually be restored, whether contact lists are current, and whether key decisions can be made without access to the systems involved in the incident.
After 90 days: build a repeatable program
Cyber resilience is not a one-time project. Review it regularly through management reporting, supplier reviews, training, recovery tests, access reviews, and lessons learned from incidents or near misses.
| Frequency | Useful control |
|---|---|
| Monthly | Review security incidents, critical vulnerabilities, privileged access, failed backups, and supplier issues |
| Quarterly | Review cyber risks with management; test selected incident-response scenarios |
| Every 6–12 months | Test backup restoration and business-continuity procedures |
| Before onboarding critical vendors | Assess security, data access, support model, incident obligations, and exit arrangements |
| After significant business change | Reassess risk when adding new sites, cloud services, integrations, production equipment, or acquisitions |
The supply-chain issue companies often miss
NIS2 explicitly makes supply-chain security a priority. This includes not only raw-material suppliers, but also the companies that support your digital operations:
- ERP and hosting providers;
- managed IT and cybersecurity providers;
- cloud platforms;
- payroll and accounting systems;
- warehouse, transport, and production-system vendors;
- software integration partners;
- remote-support providers;
- payment and e-invoicing providers.
A good supplier review should ask more than “Do you have a security certificate?” It should ask what access the supplier has, how incidents are reported, where data is hosted, how backups work, how updates are managed, whether subcontractors are involved, and what happens if the relationship ends.
A secure company can still fail through an insecure dependency.
The business case: NIS2 is resilience, not paperwork
Cybersecurity investment can feel abstract until operations stop. NIS2 forces companies to translate technical risk into business impact.
A strong program can improve:
- production and warehouse continuity;
- supplier reliability;
- customer trust;
- access control;
- audit readiness;
- recovery speed;
- internal accountability;
- ability to win enterprise contracts and public tenders;
- confidence in digital transformation projects.
The companies that benefit most will not treat NIS2 as a compliance checklist. They will use it to build a more resilient operating model.
Final thoughts: turn NIS2 into operational strength
NIS2 is a direct challenge to the old idea that cybersecurity belongs only to IT. It requires leaders to understand the systems, people, suppliers, and processes that keep the business running—and to prove that reasonable controls are in place.
For companies using SIX ERP, the opportunity is practical. Use your central operational data to map critical processes, define access roles, document suppliers, maintain audit evidence, identify business dependencies, and support faster recovery decisions.
The target is not perfect security. The target is a company that can anticipate, withstand, respond to, and recover from cyber disruption without losing control of its business.
SIX ERP can help you bring purchasing, production, warehousing, finance, CRM, approvals, and operational reporting into one connected environment—an important foundation for stronger visibility and business continuity. For a NIS2 readiness discussion, start by mapping the workflows your company cannot afford to lose.